К содержимому
learnspaceYOUR NEXT CHAPTER
ПРОСТРАНСТВО ОБУЧЕНИЯ
ГлавнаяКаталог курсовМоё обучениеCoursera

Знания без границ

Учитесь у лучших университетов и компаний мира.

Открыть Coursera
Интеграция
Пространство университета
Моё пространствоСтраница курса
↵
ЯЛичный кабинетСтудент
© 2026 LearnSpaceКаждый день — возможность узнать больше.Помощь
Advanced Threat Intelligence Techniques · LearnSpace
Назад в каталог
courseraПрограммирование

Advanced Threat Intelligence Techniques

Курс от STARWEAVER
Средний≈ 10.3 чАнглийский
О курсеНавыкиПрограммаПреподаватели

О курсе

Advanced Threat Intelligence Techniques (ATI) teaches cybersecurity professionals how to produce defensible, decision-relevant threat intelligence in real operational environments. Rather than focusing on tools alone, the course emphasizes intelligence tradecraft, guiding learners through problem framing, intelligence requirements, disciplined collection, and structured cyber threat analysis. Learners examine adversary behavior using frameworks such as MITRE ATT&CK, apply adversary modeling and TTP analysis, and evaluate evidence through structured analytic techniques. The course also explores cyber threat intelligence collection techniques, including malware analysis and OSINT collection, alongside methods for conducting careful attribution analysis while managing uncertainty and bias. Designed for SOC analysts, incident responders, threat researchers, and threat hunting teams, this advanced threat intelligence course demonstrates how cyber threat intelligence supports operational decision-making. Participants learn how to translate analytic findings into detection improvements, threat hunting hypotheses, and executive communication, while responsibly integrating emerging capabilities such as AI in cybersecurity. By the end of the course, learners will be able to produce threat intelligence assessments that withstand analytic scrutiny and meaningfully influence security operations.

Навыки, которые вы освоите

Cyber Threat IntelligenceThreat ModelingCyber Threat HuntingSecurity AwarenessCyber OperationsThreat DetectionCyber RiskCyber AttacksCybersecurityMalware ProtectionCyber Security AssessmentMITRE ATT&CK FrameworkResponsible AIThreat ManagementIntelligence Collection and AnalysisRequirements AnalysisTechnical CommunicationSecurity StrategyAI SecurityCyber Security Strategy

Программа курса

4 модулей · 70 учебных материалов

01Threat Intelligence Fundamentals and Frameworks19 материалов

Lesson 1: What is Intelligence?

Threat Intelligence Fundamentals and FrameworksDIALOGUECourse Orientation: Intelligence Tradecraft and Outcomes ВидеоWelcome to the Course: Course OverviewЧтениеModule IntroductionВидео

Учитесь у экспертов

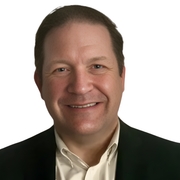
Mark Peters

DevOps and Cybersecurity Expert

Starweaver

Global Leaders in Professional & Technology Education

Advanced Threat Intelligence Techniques
В каталоге вашей программы

Инвестируйте в себя

Новые знания — в удобное для вас время.

Начать на Coursera

Обучение откроется на Coursera
в новой вкладке

Обучение на Coursera

≈ 10.3 ч

4 модулей

Язык: Английский

Часть программы вашего университета
Defining Intelligence as Decision-Support Discipline Видео
Decision-Relevant IntelligenceОбсуждение
Strategic, Operational and Tactical Intelligence Explained Видео
Applying the Intelligence Cycle to Cyber Threat Analysis Видео

Lesson 2: Shaping Intelligence Requirements

Framing the Intelligence Problem for Decision-Making ВидеоDecomposing Intelligence Questions and Assumptions ВидеоUsing MITRE ATT&CK to Structure Intelligence Problems Видео

Lesson 3: Modelling the Threat

Modeling Adversaries, Capabilities and Intent ВидеоAnalyzing Target Systems and Centers of Gravity ВидеоManaging Intelligence, Consumers, and Expectations ВидеоTradecraft Primer ЧтениеConfidence vs. SpeculationОбсуждениеHands-On-Learning: Framing Intelligence Problems and Modeling Adversary Impact Взаимная проверкаTranslating Intelligence to Leadership: Signal, Confidence, and RelevanceDIALOGUEThreat Intelligence Fundamentals and FrameworksЗадание
02Collection and Processing Techniques 16 материалов

Lesson 1: Working with Open Source

Collection and Processing Techniques DIALOGUEModule IntroductionВидеоDesigning OSINT Research Strategies ВидеоCollecting and Interpreting Dark Web Intelligence ВидеоFiltering OSINT Data for Analytic Relevance ВидеоConfidence vs. Data VolumeОбсуждение

Lesson 2: Working with Malware

Identifying and Evaluating Malware Intelligence Sources ВидеоObserving Malware Behavior Using Sandboxes ВидеоInferring Adversary Intent from Malware Behavior Видео

Lesson 3: Analyzing Data Effectively

Applying Statistical Reasoning to Threat Intelligence ВидеоVisualizing Threat Data for Analytic and Executive Use ВидеоIdentifying and Mitigating Bias in Threat Data ВидеоWhat Is OSINT (Open-Source Intelligence) in 2025? ЧтениеHands-On-Learning: From Collection to Confidence: Validating Threat Intelligence Under Uncertainty Взаимная проверкаInterpreting Malware Behavior: Evidence vs. Over-AttributionDIALOGUE
03Analysis and Attribution17 материалов

Lesson 1: Structured Analytical Techniques

Analysis and Attribution DIALOGUEModule Introduction ВидеоApplying Predictive Reasoning to Adversary Behavior ВидеоAnalyzing Adversary Organizations and Constraints ВидеоAssessing Adversary Technical Capabilities and Tradeoffs Видео

Lesson 2: Analysing Tactics, Techniques, and Procedures (TTP)

Identifying Meaningful Signals in Threat Activity ВидеоAnalyzing Adversary TTPs Using MITRE ATT&CK ВидеоAttribution Risk and Analytic RestraintОбсуждениеTranslating TTP Analysis into Defensive Use Cases Видео

Lesson 3: Compiling Intelligence Results

Producing Intelligence That Answers Organizational Requirements ВидеоExpressing Confidence and Uncertainty in Intelligence Reporting ВидеоIdentifying Intelligence Gaps and Future Collection Needs ВидеоEmergent Intelligence: Spycraft and Intelligence in the AI Era ЧтениеConfidence Levels and Intelligence TrustОбсуждениеHands-On-Learning: Evaluating Adversary Behavior and Attribution Взаимная проверка
04Operationalizing Threat Intelligence18 материалов

Lesson 1: From Intel to Tripwire

Operationalizing Threat Intelligence DIALOGUEModule Introduction ВидеоDefining Intelligence Signals for Operational Detection ВидеоInterpreting Security Reports Through an Intelligence Lens ВидеоDesigning Intelligence-Informed Security Architectures Видео

Lesson 2: Threat Hunting Approaches

Managing Legal and Ethical Constraints in Threat Hunting ВидеоCollaborating with Threat Hunters Using Intelligence ВидеоSharing Threat Intelligence Across Industry and Communities Видео

Lesson 3: Measuring Program Effectiveness

Measuring Threat Intelligence Program Success ВидеоMeasuring Intelligence Without Distorting ItОбсуждениеIdentifying Analytic, Collection, and Program Gaps ВидеоApplying AI Responsibly in Threat Intelligence Programs ВидеоFocusing on the Right Threat Intelligence Metrics ЧтениеHands-On-Learning: Operationalizing Intelligence and Measuring Impact Взаимная проверка
Collection and Processing Techniques Задание
Assessing Attribution and Tradeoffs Under UncertaintyDIALOGUE
Analysis and AttributionЗадание
Defending the Intelligence Program DIALOGUE
Course Wrap-UpВидео
Project: Producing and Operationalizing a Defensible Intelligence AssessmentВзаимная проверка
Operationalizing Threat IntelligenceЗадание